An operations director at a composite 40-person professional services firm - a pattern I've watched repeat closely enough to describe without naming anyone - walked into a March leadership meeting with a tidy spreadsheet. Eleven AI tools. Each one had an owner, a renewal date, and a name next to who had approved it. Her message to the room was reassuring: the firm did not have an AI governance problem, because it had not really rolled AI out yet.
Four days later, after someone on her team ran the corporate card statement against that spreadsheet and asked around at a Friday stand-up what people actually used to draft emails, summarize calls, or clean up a spreadsheet, the count was forty-three. Four times the eleven she had walked in with. Nobody had been hiding anything. Nobody had been asked before.
I am labeling this a composite up front - a pattern drawn from several reviews I have sat in on, not one company's ledger - because the number forty-three is less interesting than what produced it: a firm that genuinely believed it had no shadow AI problem, relying on exactly the kind of evidence I see firms this size rely on. A spreadsheet nobody had cross-checked against reality.
The Week A 40-Person Firm Found Four Times More AI Tools Than It Had Approved
The gap was not evenly spread across the business, and in my experience it rarely is. In the composite case, marketing had three separate writing assistants that nobody had mentioned to anyone else, each brought in by a different person to solve the same problem. Sales had two call-transcription tools running against client conversations, neither logged anywhere IT could see. Finance had a spreadsheet plug-in summarizing vendor contracts, quietly installed inside a workbook that two people touched. HR had a resume-screening tool a hiring manager had signed up for on a free trial eight months earlier and simply never turned off.
None of these thirty-two extra tools were exotic. Most were free tiers or personal subscriptions expensed as "software," bought by capable people trying to do their jobs faster. That is the part worth sitting with: shadow AI, in almost every version of this I have seen, is not rogue behavior. It is normal behavior in the absence of a visible, low-friction alternative.
Why Banning First Drives Usage Underground
The instinct, once a leadership team sees a number like forty-three, is to reach for a ban list. I understand the impulse. It is also, in my experience, close to the worst available next move, because a ban announced before anyone has mapped what is actually in use does not remove the tools. It removes their visibility.
Employees who were using a transcription tool openly, because nobody had told them not to, do not stop transcribing calls when a policy email goes out. They move the same tool to a personal account, on a personal device, off the corporate network where IT could have seen it at all. The firm has traded a visible problem it could manage for an invisible one it cannot. A ban written before a register is a policy solving a problem the policy's authors cannot actually see.
Governance has to follow visibility, not substitute for it. That ordering - see first, decide second - is the entire argument of this piece, and it is the reason the register comes before any policy conversation, not alongside one.
The One-Page AI Register: Five Columns That Matter
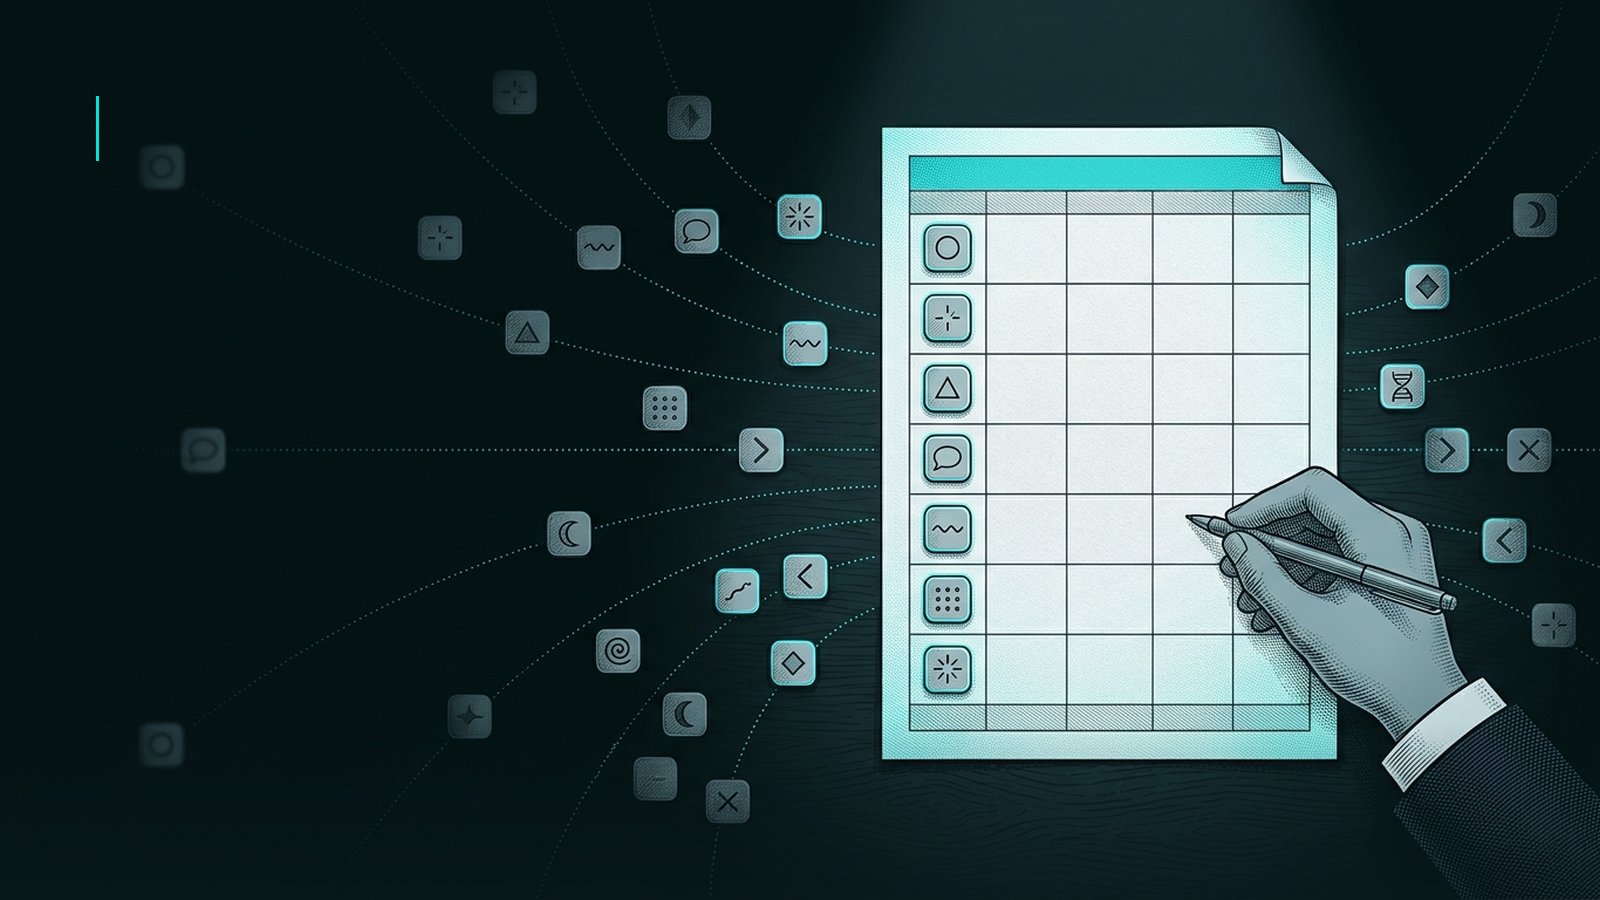
The register itself is deliberately unglamorous. One page, five columns, populated by a discovery week rather than a procurement audit:
- Tool. The specific product and vendor, not a category - the named app your sales team actually installed, not "a transcription tool."
- Department & owner. Which team uses it, and the one named person who can answer for it if asked.
- Data touched. One of four tiers: none, internal, customer, or financial - the single most useful column on the page, because it is what tells you how urgently the next two columns matter.
- Approval status. Approved, pending review, unreviewed, or flagged - a status, not yet a verdict.
- Risk tier. Low, medium, or high, set mechanically from the data-touched column plus whether the tool sits in a regulated or client-facing process - not a debate, a lookup.
Building it does not require new software or a governance committee. It requires a week and a short list of people willing to answer honestly, which is exactly what the next section is about.
- Day 1 - pull what you already have. Expensed software, corporate card statements, SSO login logs if you have them. This is the eleven-tool spreadsheet, and it is your floor, not your answer.
- Day 2 - send the discovery ask. One short message to every department, worded as an inventory, not an audit (see the next section for the exact wording).
- Day 3 - collect and reconcile. Match what people report against what the card statement and login logs show. The gaps between the two lists are where the real count lives.
- Day 4 - score data touched and risk tier. For each tool, ask one question: what is the most sensitive thing this tool has seen. That answer sets the column.
- Day 5 - circulate the page. One page, to the leadership team, with nothing decided yet - just seen.

Running Discovery Week Without Becoming the Tool Police
The wording of the ask decides whether discovery week produces an honest list or a defensive silence. If security or IT sends it, framed as an audit, people report the tools they are least attached to and quietly keep the rest off the books. The tone has to be closer to a stock take than an investigation, and it should come from someone employees do not associate with enforcement - a COO, an operations lead, in a smaller firm sometimes the founder directly.
"We're building a one-page list of every AI tool currently in use across the firm - not to restrict anything yet, just to see the full picture. If you use an AI tool for any part of your work, reply with the tool name and what you use it for. Nobody is in trouble for anything on this list. The only thing that creates a problem is a tool we don't know about."
That last line is the amnesty, stated plainly rather than implied. It works because it is true for exactly one week: the firm genuinely does not yet know what it is looking at, so there is nothing to punish yet, and saying so removes the only reason anyone would have to under-report.
What To Do With What You Find: Sanction, Migrate, Retire
Once the page exists, every tool on it sorts into one of three buckets. Sanction: the tool is fine, formalize it - an owner, a renewal date, a place in procurement's records. Migrate: the need is real but the specific tool is not, usually because it touches customer or financial data without the controls the firm already pays for elsewhere; move the workflow to an approved alternative rather than banning the underlying need. Retire: the tool was a trial nobody remembered to cancel, or a duplicate of something already sanctioned elsewhere on the page - switch it off and note why.
The register does not stay static once these three decisions are made. It earns a slot on a 20-minute monthly review - new tools added since last month, any risk tier that changed because a tool started touching more sensitive data, and a one-line decision logged against each. Twenty minutes is the deliberate constraint: long enough to keep the page honest, short enough that it survives being a permanent fixture rather than a one-time project that quietly lapses.
If I could hand that operations director one artifact before her March meeting, it would not have been a policy. It would have been this page - because you cannot govern what you have not yet counted, and in the composite case, and in the firms I have looked at closely, the counting was the part nobody had actually done.
For more on this and related work, see BrianServes, the platform for deploying autonomous AI e-mployees and Webspot, the AI strategy firm in Beirut.
Related evidence: The EU AI Act obliges providers of high-risk AI systems to report a serious incident to the market surveillance authorities immediately after establishing a causal link to the system, and in any event not later than 15 days after becoming aware of it — a disclosure deadline fixed in law rather than decided during the incident. (the EU AI Act's 15-day serious-incident reporting deadline)
The Model Cards paper proposes short documents that accompany trained machine learning models and report benchmarked evaluation across a variety of conditions. (the Model Cards for Model Reporting paper)